Two waves of MH370-themed cyberattacks
9 March official-network intrusion · March–April public malware lures
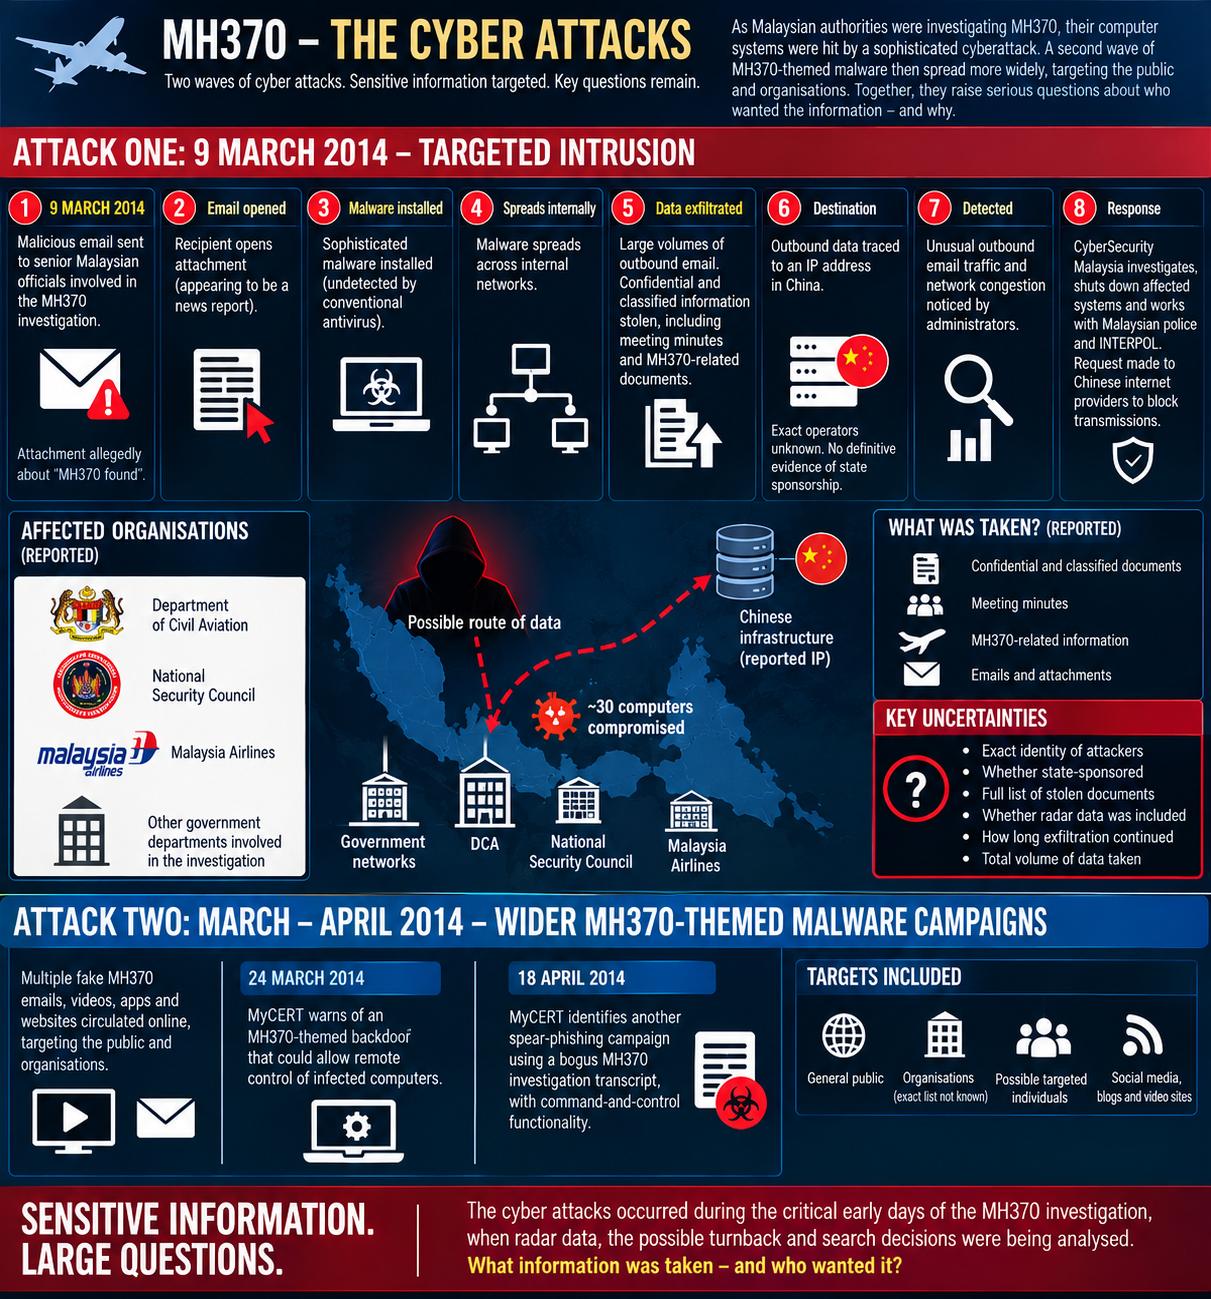
Working chart of two separate campaigns. Attack one: 9 March spear-phish of officials at the Department of Civil Aviation, National Security Council and Malaysia Airlines — CyberSecurity Malaysia’s public account, disclosed in August. Attack two: MyCERT alerts on 24 March and 18 April about MH370-themed backdoors and a fake investigation-transcript phish aimed more widely. Destination IP in China is not the same as a finding that Beijing ran the operation.
Keep the two waves apart. The 9 March job hit machines inside the investigation: about thirty computers, malware that conventional antivirus missed, outbound mail carrying minutes and classified documents, some of it MH370-related, toward an IP address in China. CyberSecurity Malaysia, police and Interpol worked the case; Chinese ISPs were asked to block the traffic. That is CSM’s account, given by CEO Amirudin Abdul Wahab to The Star and published 20 August 2014. Attack two is the public-facing MH370 lure season: MyCERT MA-381 (24 March) on a Facebook-app backdoor with remote-control capability, and MA-386 (18 April) on a spear-phish posing as an investigation team / ICAO portal item that dropped a fake transcript and command-and-control. FireEye separately logged MH370-lure spear-phish against an Asia-Pacific government and a US think tank in mid-March. None of that, on present records, names the radar feeds or proves the 9 March take included the westbound primary track. Attribution remains open: state-linked, non-state, third-party infrastructure, or false flag are all still live.
Sources
- Working chart · two waves of MH370-themed attacks
Related
The radar story and the 9 March cyberattack
Working chart · tracks, delays, and a spear-phish of the investigation
Investigation networks spear-phished the day after MH370 vanished
CyberSecurity Malaysia · ~30 PCs · disclosed 20 August 2014
MyCERT: MH370-themed backdoor and fake-transcript spear-phish
MA-381 · 24 March 2014 · MA-386 · 18 April 2014
What was actually taken on 9 March — and did it include radar?
A China IP is not a finding that Beijing ran the 9 March hack
Routing fact · operator unknown
CyberSecurity Malaysia
National cyber agency · publicly described the 9 March intrusion in August 2014