Resources
Resources
Official papers, films, Wikipedia and its citations, programmes, claims and open questions.
7 hits
A China IP is not a finding that Beijing ran the 9 March hack
Routing fact · operator unknown
CSM said exfiltrated mail went to an IP address in China. Headlines called it a Chinese hack. The agency did not publish a named operator. Compromised machines, third-party infrastructure and a false flag remain live. Not established, not ruled out.
Does the classified Lin addendum name MH370 or a satellite video?
Public FOIA production does not. The addendum is unreleased. Until it is, the leaker identification remains a Forbes attribution.
4ORBS — Ashton Forbes video knowledge base
Third-party extract of 824 videos · a claim list, not proof
Structured archive extracted from 824 Ashton Forbes videos. Distinguishes extracted claims from proof. Every material proposition still has to be traced to the original document or video.
Alleged-video 6 fps ‘Gorgon Stare match’ is contradicted by the 2013 OSD report
The 6 fps ‘Gorgon Stare match’ claimed for alleged video is not established. 2 fps is the documented comparison figure. Increment 2’s rate is unpublished here.
CyberSecurity Malaysia
National cyber agency · publicly described the 9 March intrusion in August 2014
Confirmed. Agency under the then Ministry of Science, Technology and Innovation. CEO Amirudin Abdul Wahab is the named source for the 9 March spear-phish of investigation officials. Digital forensics support to the affected departments; work with police and Interpol.
Investigation networks spear-phished the day after MH370 vanished
CyberSecurity Malaysia · ~30 PCs · disclosed 20 August 2014
Confirmed as CSM’s public account. On 9 March, officials at the Department of Civil Aviation, the National Security Council and Malaysia Airlines were sent malware disguised as a news article that the aircraft had been found. About thirty computers were infected. Outbound mail carrying confidential files, including meeting minutes and classified documents, some related to MH370, was traced to an IP in China. CSM shut the machines down and asked Chinese providers to block the traffic. Police and Interpol were involved. What exactly was stolen is still unpublished.
Two waves of MH370-themed cyberattacks
9 March official-network intrusion · March–April public malware lures
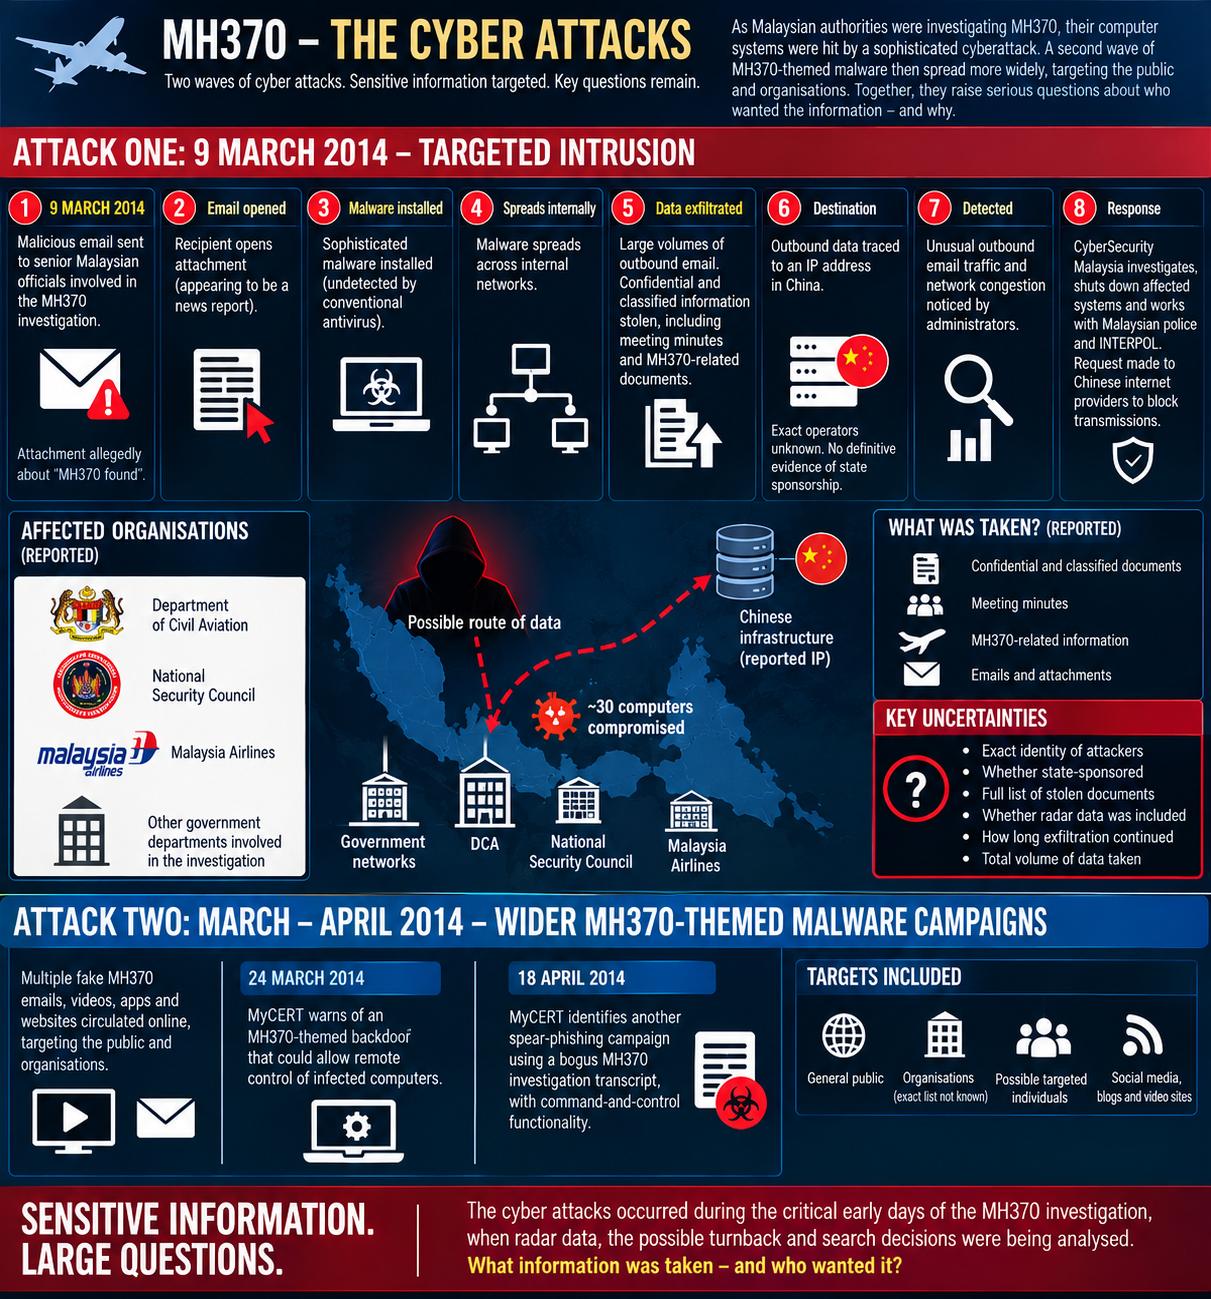
Working chart of two separate campaigns. Attack one: 9 March spear-phish of officials at the Department of Civil Aviation, National Security Council and Malaysia Airlines — CyberSecurity Malaysia’s public account, disclosed in August. Attack two: MyCERT alerts on 24 March and 18 April about MH370-themed backdoors and a fake investigation-transcript phish aimed more widely. Destination IP in China is not the same as a finding that Beijing ran the operation.
273 records in the file.