Resources
Resources
Official papers, films, Wikipedia and its citations, programmes, claims and open questions.
12 hits
Angel Fire
Wide-area airborne surveillance · lineage into Blue Devil Block 1
USAF/SOCOM WAAS system. Congressional documentation describes Blue Devil Block 1 as integrating Angel Fire-derived wide-area imagery with signals intelligence on manned aircraft. Confirmed as the WAAS ancestor in this family, not as an MH370 collector.
Cargo, including lithium-ion batteries
Manifest reviewed; fire hypothesis not supported
The aircraft carried cargo including lithium-ion batteries. The investigation found they were packed to regulation and did not support a cargo-fire cause.
Mechanical / cargo-fire failure
Official report: no identified failure mode fits
A running systems failure that also produces a coherent reverse course and six more hours of SATCOM is a poor fit. Lithium-battery cargo was reviewed and not adopted as cause.
Blue Devil I / II
Operational Block 1 WAAS + SIGINT · Block 2 residuals to BIG SAFARI
Block 1 was operational: manned aircraft carrying Angel Fire-derived wide-area imagery integrated with SIGINT. Block 2, the airship, was terminated — but its equipment, including GFE, was packed and sent to a BIG SAFARI facility in Greenville, Texas, available for other programmes. The technology did not vanish with the airship.
A BIG SAFARI collection architecture around MH370
The family is documented. A specific 8 March operation is open.
Gorgon Stare, Blue Devil and MAGIC/Orion are one overlapping ISR family under 645 AESG / BIG SAFARI: same office, overlapping WAMI/SIGINT sensors, reusable GFE through Greenville, and a podded architecture meant to move between airframes. That family is confirmed. Whether any of it collected MH370 is not established and is not ruled out.
Blue Devil I operational demonstration ends
31 December 2013 · four King Airs returning to Leidos
Attributed via Inside the Air Force, 22 Jan 2014, quoting USAF officials. The four leased King Airs were returning to Leidos, so the original Afghanistan fleet was not an operational candidate on 8 March 2014. The multi-INT sensor package remained US Government property and was being assessed for reassignment (MC-12 and MQ-9 mentioned, not selected). The sensors did not disappear with the lease.
Can the Motorola and mangosteen cargo be rebuilt at carton level?
Working-log Q28–Q35: airway bill 232-10677085, Motorola SKUs, whether radios/transmitters were present, CG effects, and why the Motorola consignment was not X-rayed.
Gorgon Stare, Blue Devil and MAGIC/Orion are one overlapping ISR family under BIG SAFARI
Confirmed by Congressional and USAF budget records. Same office, overlapping sensors (WAMI, SIGINT, airborne processing), shared GFE path through Greenville, and a podded architecture meant to move between airframes. Not isolated programmes that happen to share a decade.
Malaysia releases the safety investigation report
30 July 2018
The ICAO Annex 13 team, led by Kok Soo Chon, publishes hundreds of pages and cannot determine the cause. Diversion is judged likely from manual inputs. Third-party intervention is not excluded.
MyCERT: MH370-themed backdoor and fake-transcript spear-phish
MA-381 · 24 March 2014 · MA-386 · 18 April 2014
Confirmed public advisories, a different campaign from the 9 March official-network intrusion. 24 March: a Facebook-app lure dropping a backdoor with remote-control (C2) capability. 18 April: emails posing as an investigation team / ICAO portal item, password-protected archive, fake MH370 transcript, command-and-control. Aimed at organisations and the public, not shown to be the DCA/NSC/MAS breach.
No 406 MHz ELT detection
Emergency locator transmitter never heard
No satellite or ground station reported a 406 MHz distress burst from 9M-MRO. Compatible with a high-energy impact, a powered-off ELT, or a failure to trigger.
Two waves of MH370-themed cyberattacks
9 March official-network intrusion · March–April public malware lures
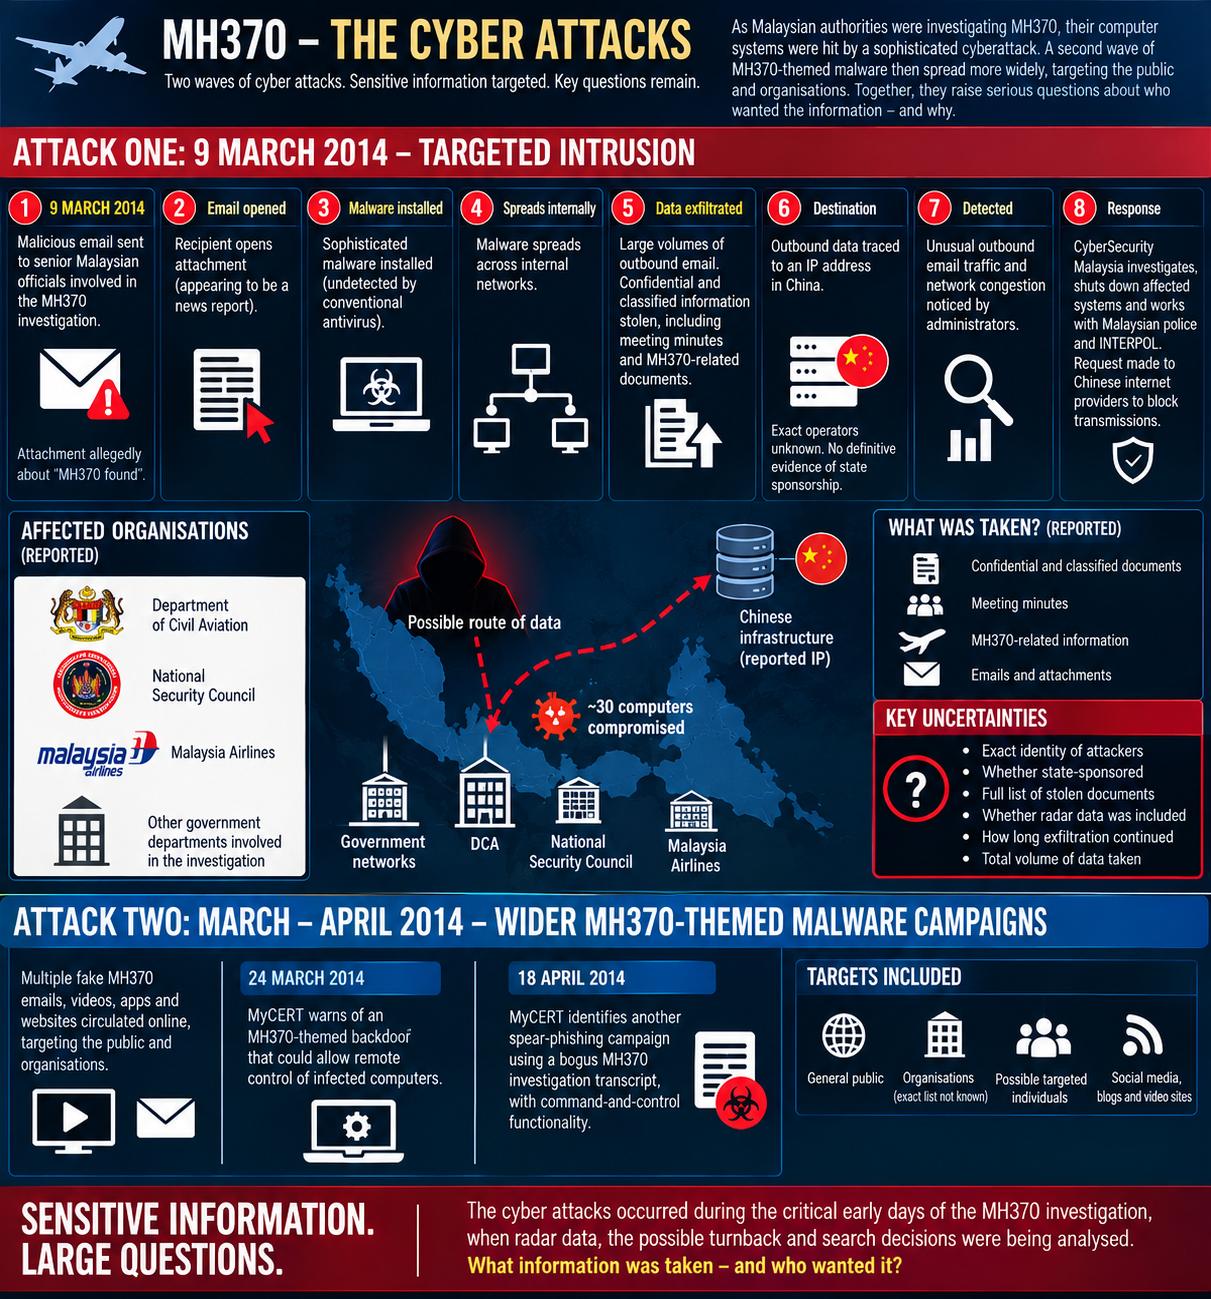
Working chart of two separate campaigns. Attack one: 9 March spear-phish of officials at the Department of Civil Aviation, National Security Council and Malaysia Airlines — CyberSecurity Malaysia’s public account, disclosed in August. Attack two: MyCERT alerts on 24 March and 18 April about MH370-themed backdoors and a fake investigation-transcript phish aimed more widely. Destination IP in China is not the same as a finding that Beijing ran the operation.
273 records in the file.